Blog: Insights, updates & innovations shaping the future
Stay ahead with the latest features, upcoming releases, and expert insights that keep you informed and empowered.
Why Keys Belong in an HSM: Crypto APIs Explained
Why private keys belong in a hardware security module, how applications reach HSMs through PKCS#11, JCE and REST crypto APIs, and how to design a central crypto service.
Read MoreWhat Is Certificate Lifecycle Management? A Plain-English Guide for 2026
Certificate lifecycle management (CLM) finds, tracks, renews and retires every certificate you use. Learn the five lifecycle stages, why CLM matters more in 2026 and how to start.
Read MoreHow RFC 3161 Timestamping Proves When a Document Was Signed
An RFC 3161 timestamp binds a document's hash to a trusted time, signed by a Time Stamping Authority. Learn how tokens are issued and verified, where they are used and what eIDAS says about them.
Read MorePrivate CA vs Public CA: Which Certificates Should You Issue Yourself?
Public CAs secure what outsiders must trust; private CAs secure what you control. Compare trust, rules, lifetimes, cost and risk, and see which certificates to issue yourself.
Read MoreRecent posts
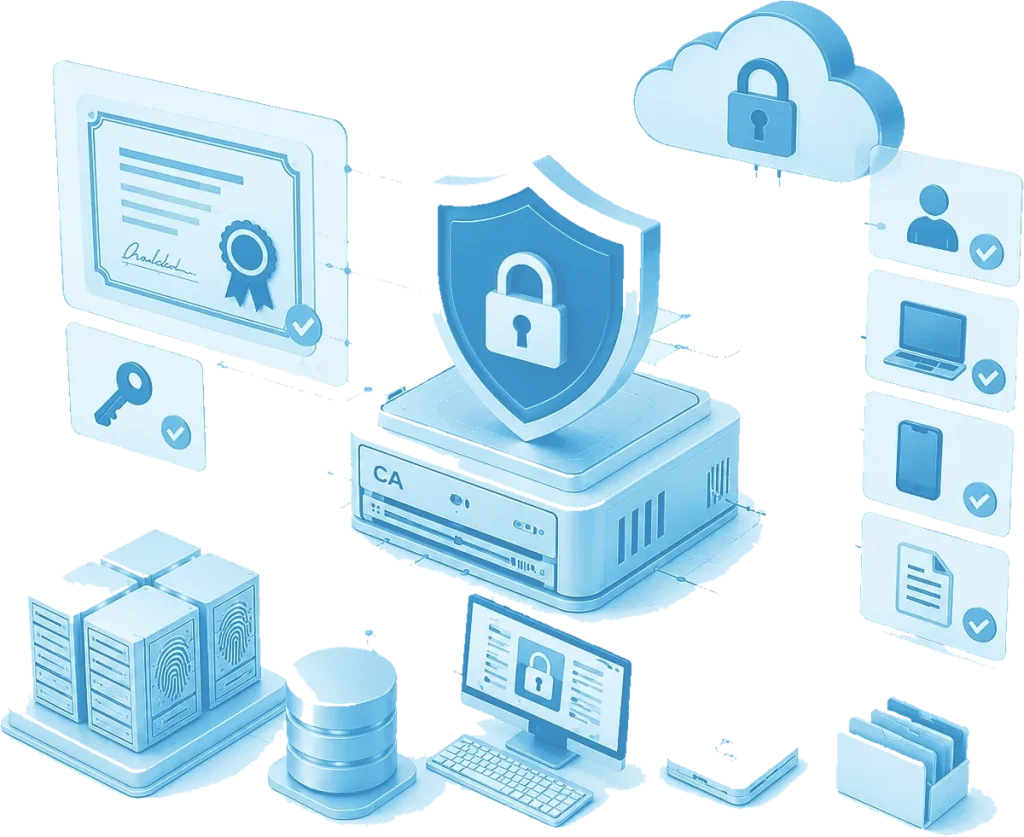
Why Keys Belong in an HSM: Crypto APIs Explained


How RFC 3161 Timestamping Proves When a Document Was Signed


The 10-Point PKI Health Check: Find Outage Risks Before They Hit

Why Keys Belong in an HSM: Crypto APIs Explained


How RFC 3161 Timestamping Proves When a Document Was Signed


The 10-Point PKI Health Check: Find Outage Risks Before They Hit
Have a question?
Let’s discuss your unique identity challenges and find the perfect solution together.
- USA: 651 N Broad St, Suite 201, Middletown, DE 19709, USA
- PAK: 26 Block G4 Rd, Phase 2, Johar Town, Lahore, Punjab, Pakistan
- +1 352-451-6005
- info@dictalabs.com
Start here
Explore PKI topics
Our guides explain PKI, certificates, timestamping, digital signatures and post-quantum readiness in plain English. Start with a topic below, or open the PKI Resources hub for the full library and glossary.
Certificate lifecycle
PKI and certificate authorities
Timestamping and signatures
Keys, HSMs and post-quantum
Trust services and eIDAS
Identity and access
Each guide answers its question in the first lines, then explains the details and names the standards it relies on, such as RFC 3161, RFC 5280, ETSI EN 319 421 and eIDAS. Looking for a quick definition instead? The PKI Resources glossary covers PKI, certificate lifecycle management, HSMs, RFC 3161 timestamps and qualified trust service providers.